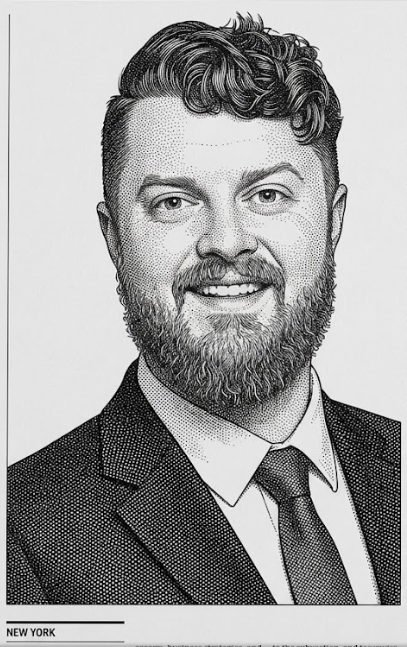
AI governance and vendor risk, run by one person who has done it.
When a customer's security questionnaire asks about your AI use, you need a policy, a risk process, and someone accountable. I build them and run them. I wrote Autodesk's third-party AI risk criteria, and closed every assessment aged past 90 days in a vendor-risk program that was 120 days behind its SLA.
Three disciplines. One accountable partner.
Engage me for ongoing fractional support or a defined-scope project — whichever matches where your organization is today.
IT & Infrastructure Leadership
Hands-on technology leadership for companies that need senior direction without a full-time executive hire.
- IT strategy, roadmap, and budget ownership
- Data center, cloud, and infrastructure operations oversight
- Business continuity & disaster recovery planning
- Vendor, MSP, and internal team management
- Capacity planning and system reliability (uptime, monitoring, redundancy)
- Technology due diligence for M&A and vendor consolidation
Governance, Risk & Compliance
Practical GRC programs built around recognized frameworks — sized to your team, not a Fortune 500 department.
- Third-party / vendor risk management program design
- SOC 2, ISO 27001, NIST 800-53 & NIST CSF control mapping
- Security questionnaires, SIG assessments & residual risk reporting
- Executive and board-level risk reporting
- Policy, process & procedure development
- GRC tooling: ServiceNow VRM, OneTrust, RiskRecon, BitSight
AI Policy, Program & Training
AI governance programs that keep pace with adoption — policy, risk criteria, and training, not shelfware.
- AI use policy development
- AI risk criteria & model risk assessment
- AI governance program design — intake, approval workflows, oversight
- Training & enablement
- Vendor & third-party AI risk
- Executive & board reporting on AI risk
Built for accountability, not busywork
Executive-ready reporting
Risk and operational posture communicated in language business stakeholders and boards can act on, not just technical teams.
Metrics over meetings
Programs are run against clear SLAs and measurable outcomes: risk closure rates, uptime targets, and backlog reduction — not status theater.
Framework-grounded
Every engagement maps to recognized standards — NIST 800-53, NIST CSF, FFIEC, PCI, ISO 27001, SOC 2 — so controls hold up to audit and stakeholder scrutiny.
Experience
Track record leading IT operations and third-party risk programs at a global SaaS platform and a $1B+ financial institution.
Third-Party Risk Manager
Led combined US/India teams to close 100% of open vendor risk items within SLA; built Autodesk's third-party AI risk criteria and 3-year TPRM strategy; delivered quarterly risk reporting to the executive committee.
Associate Vice President, IT Service Delivery
Owned all data center operations and cybersecurity programs for a $1B+ credit union; maintained 99.99% uptime; managed six internal and external teams; built the credit union's first secure ACH transmission room and 24/7 incident response operation.
IT Service Delivery Manager & IT Operations Manager
Wrote the credit union's first disaster recovery plan, led a 50+ application data center migration, deployed its first Web Application Firewall, and migrated critical infrastructure from Windows Server 2003 to 2016.
Before you book a call
Fractional CTO, GRC, and AI governance — three disciplines few providers combine under one relationship.
What does a fractional CTO do?
A fractional CTO owns technology strategy and infrastructure decisions the way a full-time CTO would: IT roadmap, budget, vendor management, business continuity. It's sized to what your organization needs right now, not a full-time seat.
What does a fractional GRC advisor do? Is that the same as a virtual CISO (vCISO)?
A fractional GRC advisor builds and runs your governance, risk, and compliance program: third-party risk, SOC 2/ISO 27001/NIST control mapping, policy development, board-level risk reporting. It overlaps with what's often called a virtual CISO, though GRC is the more accurate term for the scope — program and controls ownership, not incident response or managing a security team.
What does fractional AI governance cover?
AI use policy, risk criteria for evaluating tools and vendors, governance program design, and the training that makes a policy actually get followed instead of just filed. It's often paired with GRC work, since AI risk is increasingly part of a broader risk program, but it stands on its own when AI adoption has outpaced everything else.
How is this different from hiring a consultant who writes a report and leaves?
Every engagement starts with your own framing of the problem you're trying to solve, not a standard package, and is judged on the deliverables and outcomes that move the needle, not hours logged. I own the program the way an in-house hire would, for as long as the engagement runs.
How much does a fractional engagement cost?
It depends on scope, not a fixed menu — a narrowly-defined project and an ongoing fractional seat are priced very differently. Book an introductory call and I'll give you a straight answer once I understand what you're trying to solve.
Do you work with companies outside Asheville, NC?
Yes. I'm based in Asheville, NC and available remotely for organizations anywhere.
Ready to bring senior IT and GRC leadership in-house — fractionally?
I take on a limited number of clients at a time so every engagement gets real attention. Reach out to discuss scope, cadence, and fit.